We recently found an article highlighting how national foodservice equipment supply company Edward Don & Company was forced to temporarily shut down some of its operations last year due to a Phishing attack. The article noted that the ransomware attack was likely caused by Qbot malware, typically delivered through email phishing.
Given the disruption this attack caused Edward Don’s business operations, we want to alert our foodservice equipment supply company clients about the dangers of phishing. A successful phishing attack can cost small- to medium-sized businesses more than $1 million to resolve, which would be devastating for any of Beedash’s FES partners. Read on to learn how to protect your business and customers from email phishing.
What is a Phishing Scam?
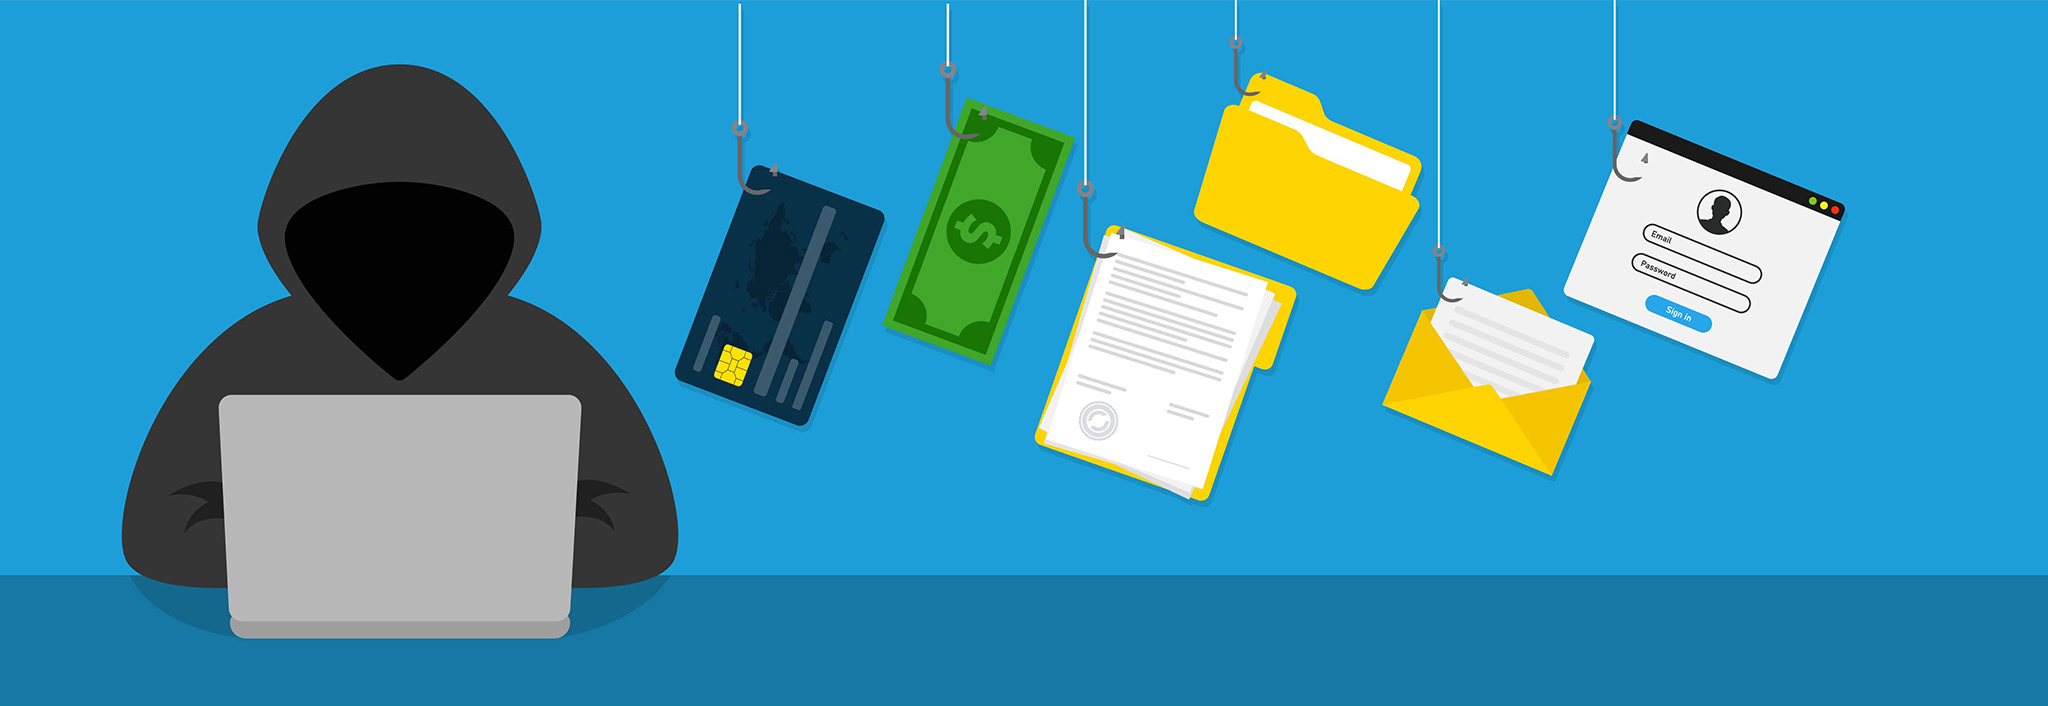
Phishing is a type of cybercrime committed by scammers who entice individuals to divulge confidential information or allow malware entry into company computer systems. Such phishing scams have long utilized fake emails that trick targets into providing necessary information like banking data, personal identification info, passwords, and other information that can facilitate cybertheft of assets or information. Phishing emails may also contain a fake link or attachment that installs malware (malicious software) into the target computer system.
With millions of identified malware variants, this malicious software can wreak havoc on a company’s computer system and business. The purpose behind many common malware attacks include:
- Steal company data
- Encrypts or locks data to hold it for “ransom”
- Access financial data to initiate cybertheft
- Alter or hijack core computer functions
- Delete data
- Alter data
Like traditional rod and reel fishing, phishing relies on bait. If the target does not go for the bait by responding to the email, opening fake links, or filling out any requested information, the scammer’s phishing expedition will be a bust. In recent years, scammers have expanded their phishing attempts via text messaging and telephone calls.
Common Types of Phishing
Much like there are different kinds of fishing—surf, deep-sea, fly, float, bottom, spear, etc.—there are numerous types of phishing. The most common forms include:
Basic Phishing—this one has been around since the early days of our digital age and entails mass email (or texting) campaigns that entice thousands of targets in one fell swoop. While there are many variations, basic phishing campaigns often send emails to appear to be from a credible source—such as a bank, major company, or the IRS—and tend to represent an emergency or other sense of urgency. For example, a bank-related scam might state that your account has been hacked and insist that you reset your password or validate your identity. A company-related scam might say that a valuable rebate is about to expire or that they have an undelivered package for you. This bait is used to get you to click a link, attachment or fill out specific information the scammer can use to further the goals of the scam.
Spear Phishing—spear phishing tends to be more sophisticated in that it targets specific individuals via email, text, or phone calls purportedly from a trusted source, such as a co-worker, HR department, client, contractor, or other entity linked to the target’s business. A common goal of spear phishing is to gain access to company information or the company’s computer system. While the bait is similar, scammers put much more effort into making it appear to be authentic.
Whaling—This type of phishing targets the biggest fish. That is top executives within a company. As such, scammers also make a serious effort to make it seem like the communications are coming from a trusted source, such as another executive or other person with close business ties to the target. They do this by conducting extensive research on the company and its employees and by taking the time to customize just the right realistic-looking messaging to make the target take the bait.
Identifying a Phishing Email
Many phishing scams are relatively easy to identify. Because many basic phishing attacks come from overseas, related emails often contain spelling and grammar mistakes. This is a significant tip-off, but you should also be wary of emails or texts promoting a sense of urgency. Think, did your account really get hacked? You can easily check before taking any requested action from the email or text communications.
It would be best always to treat attachments and links with skepticism, so double-think before clicking on them. You can hover your cursor over any links before clicking to expose the URL to determine where it might take you. If it doesn’t look legit, or the URL’s “HTTPS” is missing the “S,” it’s probably bogus. Phishing attachments often carry odd names and usually have file name extensions that can identify them as potential malware. Common malware file extensions include .zip, .exe, .bat, .scr, .dxz, and a host of others which can be reviewed here.
Ways to Protect Your FES Company From Email Phishing
Phishing attacks are only successful when you or others in your company take the bait. To help protect your FES company from the potential damage caused by a phishing attack, consider taking these measures:
- Train everyone in your company about the dangers of phishing and how to recognize potentially fraudulent emails, text messages, and phone calls.
- Explore email filter options offered by your email provider.
- Make sure you keep your anti-virus software and spam filters up to date.
- Regularly update system passwords used by everyone in the company.
- Initiate company-wide password changes whenever a system security breach or incident occurs.
- Encrypt all of the company’s sensitive files.
- Make use of secure browsers.
Turn to Beedash for All Your Digital Marketing Solutions!
We trust this article will help protect your FES company from phishing attacks. With more than 10 years of website development and digital marketing experience for the foodservice equipment supply industry, Beedash is committed to providing our dealer clients with the most advanced software solutions and digital marketing services.